

The Register über SySS-Auftritt in Australien
–
 In the Media In the Media
Führendes britisches IT-Security-Nachrichtenportal berichtet über Vortrag von Gerhard Klostermeier auf der Ruxcon
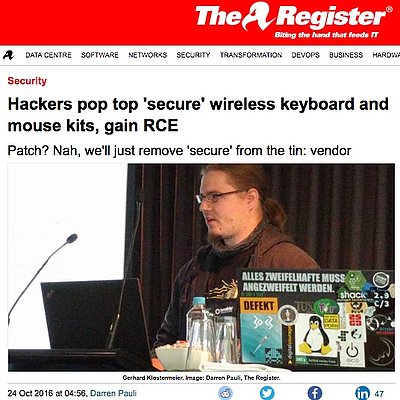
"Wireless keyboard and mouse manufacturers including Microsoft, Fujitsu, and Logitech have been forced to fix borked encryption in peripherals that allow physical attackers to hijack computers. Researchers and phDs Gerhard Klostermeier and Matthias Deeg with Germany-based security firm SySS tested five devices badged as secure including the Cherry AES B.Unlimited and Perixx Periduo-710W. Klostermeier demonstrated to the Ruxcon hacking confab in Melbourne how each test subject permitted keystroke injection, mouse spoofing, replay attacks, and all but the Logitech set up had lax code protections."
Den ganzen Artikel finden Sie hier.
Auch das italienische IT-Portal Security Info berichtet über "Radioactive Mouse".
Termine
14.09.2026
Secu5: Planung und Durchführung von Penetrationstests
15.09.2026
- 17.09.2026
Hack3: Angriffe auf Windows-basierte Netzwerke
15.09.2026
Awe2: Phishing Awareness
16.09.2026
Awe1: IT-Sicherheit kennenlernen
Ihr direkter Kontakt zu SySS +49 7071 407856-9107 oder anfrage@syss.de | Sie haben einen Cybersicherheitsvorfall? +49 7071 407856-99
Ihr direkter Kontakt zu SySS +49 7071 407856-9107 oder anfrage@syss.de
Sie haben einen Cybersicherheitsvorfall? +49 7071 407856-99
Direkter Kontakt
+49 7071 407856-9107 oder anfrage@syss.de
Sie haben einen Cybersicherheitsvorfall?




